> For the complete documentation index, see [llms.txt](https://docs.powermonitor.com.br/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.powermonitor.com.br/en/readme/como-instalar-o-power-monitor/instalacao-automatica.md).
# Automatic Installation
Step-by-step guide to the Power Monitor automatic installation: consents, creation of the application in Entra ID, acceptance of the terms, additional permissions, capacity metrics source and workspac
In the **Automatic Installation** (recommended), the Power Monitor wizard configures everything in your tenant for you: it creates the **App Registration**, the **Service Principal**, the **client secret** and a **security group**, and applies the **Fabric tenant settings** that enable the admin APIs for this application.
This page continues from the **Installation Type** step. The previous steps (region, organization and billing) are in [How to install Power Monitor?](/en/readme/como-instalar-o-power-monitor.md)
{% hint style="info" %}
**Who should run it:** an Entra ID **Global Administrator** account (or one with permission to register applications, create groups and grant admin consent). For the Fabric tenant settings to be applied, the same account must also be a **Fabric (Power BI) Administrator**. If it is not, the installation completes with a pending item, which a Fabric administrator resolves later (see step 3).
{% endhint %}
The automatic mode track has 9 steps: **Organization › Billing › Installation › Permissions › Automatic › Additional Permissions › Metrics Source › Workspaces › Done**.
***
## Step by step
{% stepper %}
{% step %}
### Required Permissions
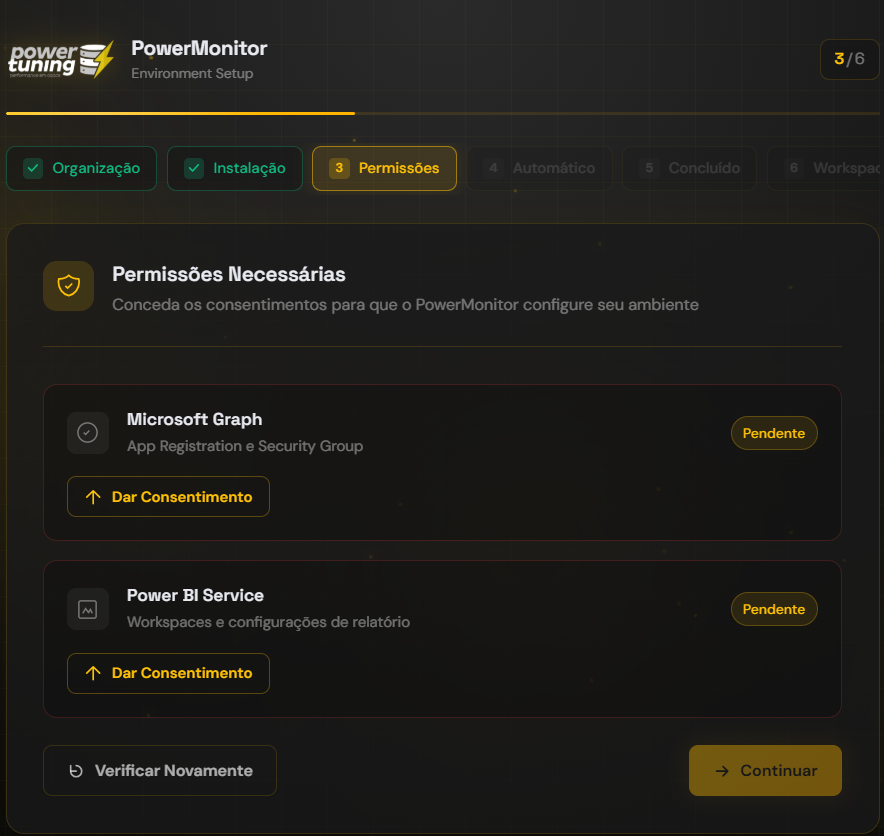
On the **Required Permissions** screen, grant the two admin consents that the wizard uses **during** the installation:
| Card | What it is for |
| --------------------------------------------------------- | ------------------------------------------------------------------------------------------------- |
| **Microsoft Graph** (App Registration and Security Group) | Create the application, the Service Principal, the secret and the security group in your Entra ID |
| **Power BI Service** (Workspaces and report settings) | Apply the Fabric tenant settings and list the tenant's workspaces |
Click **Grant Consent** on each card. In the Microsoft window, **check the "Consent on behalf of your organization" option** before accepting: without it, the status remains **Admin Consent Pending** and the installation cannot continue. In that case, use **Grant Again (with Admin Consent)**.
The wizard checks the status automatically every 10 seconds. If a card does not change to **Granted**, click **Check Again**. With both granted, click **Continue**.
Microsoft Graph and Power BI Service consents
{% hint style="warning" %}
If the browser blocks the consent window, allow pop-ups for Power Monitor and click again.
{% endhint %}
{% endstep %}
{% step %}
### Start Installation
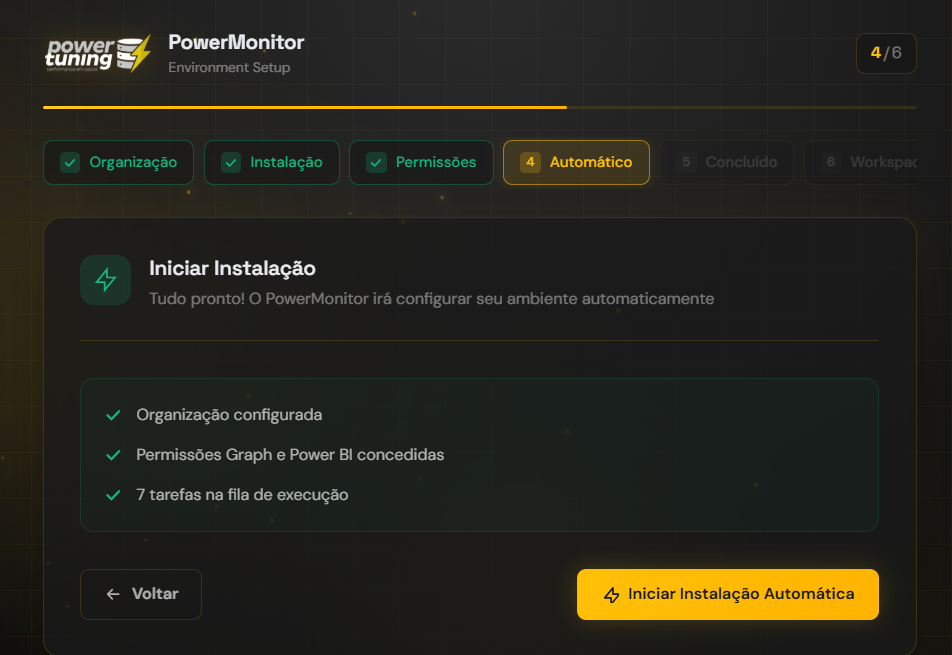
Review the summary and click **Start Automatic Installation**. The **Setting Up Azure Environment** window shows the progress of each task:
1. **Create App Registration**
2. **Create Service Principal**
3. **Generate Client Secret**
4. **Create Security Group**
5. **Add to Group** (the Service Principal joins the security group)
6. **Configure Power BI** (applies the Fabric tenant settings to the group)
7. **Save Credentials** (the credentials are stored encrypted in Power Monitor)
At the end, the wizard also **removes the temporary permissions** granted in the previous step, which were only needed for the installation.
Automatic installation progress
{% endstep %}
{% step %}
### Check the result of the Power BI configuration
The **Configure Power BI** task separates the tenant settings into **required** and **optional**:
* **Everything applied:** the installation proceeds normally.
* **Optional settings not applied:** the installation proceeds; some specific features may be unavailable until they are enabled.
* **Required settings not applied** (for example, because the account used is not a Fabric administrator): the installation **completes anyway**, with the notice *"Installation completed with pending items"*. **Data collection does not work** until a Fabric administrator enables these settings.
{% hint style="danger" %}
Do not redo the installation because of this notice: the credentials have already been saved. Ask a Fabric administrator to complete the step in **Settings › Additional Permissions › Basic Fabric permissions**, or to manually enable the settings listed in [Prerequisites](/en/technical-documentation/instalacao/pre-requisitos.md#fabric-tenant-settings) in the Fabric admin portal.
{% endhint %}
{% endstep %}
{% step %}
### Terms of Acceptance
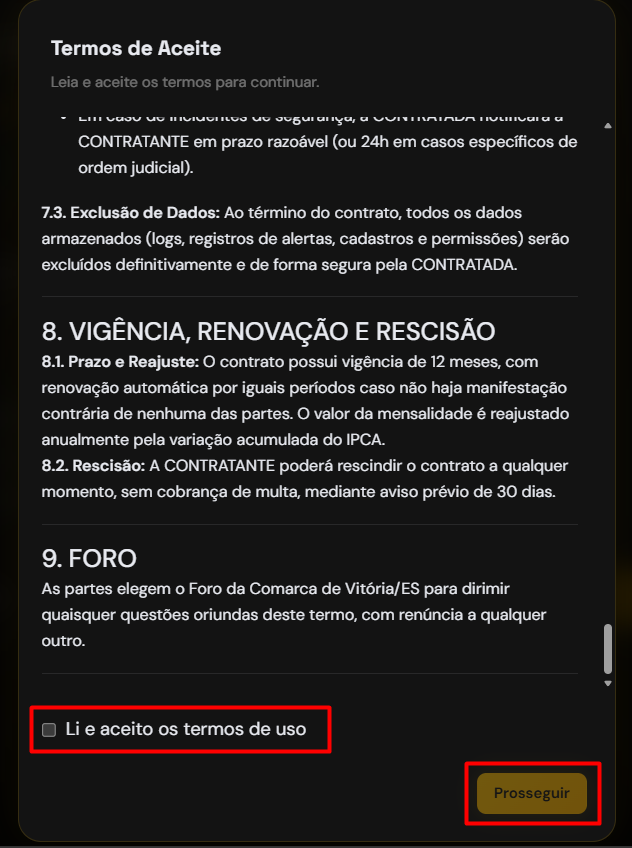
Read the **Terms of Use, Privacy Policy and Commercial Terms**, check **I have read and accept the terms of use** and click **Proceed**. Acceptance **activates the organization**: from this point on, the 30-day trial period is in effect and exiting the wizard no longer deletes anything.
Accepting the terms
{% endstep %}
{% step %}
### Additional Permissions (optional)
Grant now the optional permissions that unlock extra features. Each permission is granted **with the account of the person who clicks**, who must have the role indicated for each group:
| Group | Permission | What it unlocks |
| ----------------------------------------------------------------------------------------------------- | ---------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Microsoft Fabric permissions** (Fabric Administrator; for gateways, also a gateway administrator) | **Gateways and connections** | Service Principal as gateway administrator and user of connections without a gateway, to monitor gateways and map connections |
| **Microsoft Entra ID (Graph) permissions** (Global Administrator or Privileged Role Administrator) | **App secret expiration** | Reads the client secret expiration date, to warn you before it expires |
| | **Entra ID user import** | Reads users, groups and members; enables the "Import from Entra ID" button in Users and group expansion on the permissions screens |
| | **Sensitivity labels** | `SensitivityLabels.Read.All` permission, which only reads the Microsoft Purview label definitions (never the labeled content), to display the label names in [Labels and Certification](/en/power-monitor/governanca/conformidade/rotulos-e-certificacao.md) |
| | **Power BI licenses** | `LicenseAssignment.Read.All` and `User.Read.All` permissions, which only read the subscriptions and the licenses assigned to each user, for the [Power BI Licenses](/en/power-monitor/governanca/tenant/licencas-power-bi.md) screen. Since the automatic installation already grants `Directory.Read.All`, which covers this read, the card usually already shows as granted |
| | **Microsoft Teams bot** | Authorizes the Power Monitor bot to send alerts to the organization's Teams channels |
| **Azure permissions** (Owner on the capacities' subscriptions, or an equivalent combination of roles) | **Capacities (Governance)** | Service Principal as Administrator and Contributor of the capacities, and read access (Reader) to the subscriptions, to pause, resume and change the size (SKU) of capacities |
| | **Capacity Cost** | **Cost Management Reader** role on the subscriptions, to read the cost of each capacity |
The **Grant all needed permissions** button runs all the grants in sequence, showing the status of each one. You can **Continue** without granting anything (the wizard asks for confirmation) or **Skip** the step: everything can be done later in **Settings › Additional Permissions**.
* **Capacity Cost** depends on **Capacities (Governance)**: if the latter fails, the cost card shows a dependency error (not "Not applicable") and is granted right after, when you click **Try again** on the capacities permission. The **Cost Management Reader** role is only granted on subscriptions that have a Fabric or Power BI Embedded capacity.
* When you grant **Capacity Cost** through the wizard, Power Monitor already tests the access: the [Capacity Cost Scan](/en/power-monitor/mapeamento/custo-de-capacidade.md) is enabled without having to test the connection later in Settings. A newly created assignment that is still propagating in Azure counts as granted.
* Every **Try again** rereads the state of all cards.
{% endstep %}
{% step %}
### Metrics Source (optional)
Capacity consumption (Capacity Units) is read from the **Microsoft Fabric Capacity Metrics** app, installed in your tenant. In this step:
1. If prompted, click **Authorize Power BI access** so the wizard can look for the app in the tenant's workspaces.
2. Choose the **Workspace** where Fabric Capacity Metrics is installed and its **Semantic model**.
3. Click **Save and Continue**.
When you save, the Service Principal is added as an **Administrator** of that workspace and **consumption monitoring is turned on automatically for all capacities**. Since the installation capacity scan runs in parallel, capacities that only show up in the inventory later (in the first hours, up to about 5 hours after installation) are also turned on automatically. If, after that period, *Settings › Monitoring* still does not list a capacity, turn it on manually (see [Enable Capacity Monitoring](/en/power-monitor/monitoramento/capacidades/ativar-monitoramento-de-capacidade.md)).
{% hint style="info" %}
If no workspace with Fabric Capacity Metrics is found, install the app from Power BI AppSource and click **Check again**, or skip the step and configure it later in **Settings › Monitoring** (**Capacity Metrics Source**). If the app is outdated, reinstall it to get the current version.
If the app in the selected workspace has no capacity loaded yet (for example, because it was just installed and its data connection was not finished), *The Fabric Capacity Metrics App in this workspace has no capacity loaded yet...* is displayed. Open the app in Power BI, finish connecting its data, wait for the semantic model to refresh and click **Try again**, or click **Skip** and set it up later in *Settings › Monitoring*.
{% endhint %}
{% endstep %}
{% step %}
### Select Workspaces
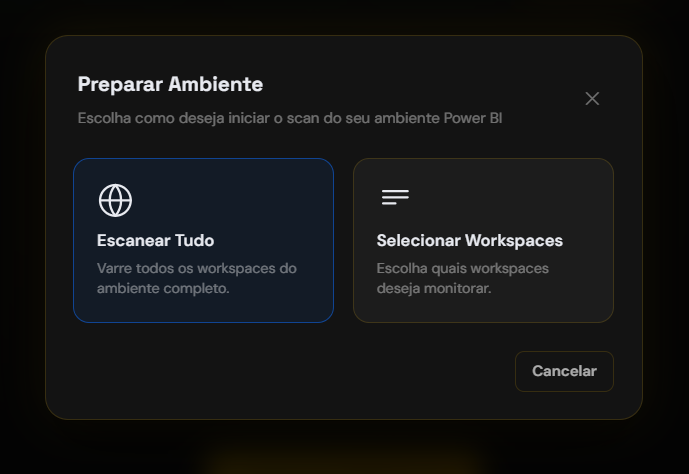
Choose which workspaces will be monitored. Use the search by name, **Select all** or **Clear selection**:
* **All selected** (**Scan Full Environment** button): all workspaces are monitored, and those created in the future are also included in monitoring automatically.
* **Some selected** (**Prepare Environment (N)** button): only the chosen ones are monitored. New workspaces discovered later are added **outside** monitoring, until an administrator includes them.
When preparing the environment, the Service Principal is also added as an **Administrator** of the chosen workspaces.
{% hint style="warning" %}
The choice affects billing: only items from monitored workspaces are counted. See [What counts as an artifact?](/en/perguntas-frequentes/licenciamento/o-que-e-contado-como-artefato.md)
{% endhint %}
Workspace selection
{% endstep %}
{% step %}
### Environment preparation and completion
Power Monitor starts the first scans (capacities, workspaces, gateways, connections and apps) and shows the environment preparation screen with the real progress:
* the **Initial scans** list, with one row per scan and the phase of each one: **Queued**, **Running** (with the processed items, for example *12 of 40*) or **Retrying**;
* the overall bar with the percentage and the summary *4 of 6 finished*. The bar never goes backwards, even when a scan goes back to the queue;
* the headline with what is running now (for example, *Scanning workspaces*) or *Queued: waiting for the collection service to start the scans*.
Independent scans (capacities, workspaces, apps and gateways) start together and right away, without waiting for the 5-minute cycle of the collection service; the ones that depend on others (connections and semantic model connections) start as soon as their prerequisite finishes.
At the end, the headline shows the outcome:
| Message | What it means |
| ----------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------- |
| *All set, shall we start?* | All initial scans finished. |
| *Environment configured, but some scans failed.* | The environment is ready; the scans that failed are listed and run again in the daily automatic collection. |
| *Environment configured. The initial collection continues in the background.* | The screen closed before all of them finished. The data shows up in the dashboard and in the inventory screens as each scan finishes. |
| *Environment configured. Progress could not be tracked.* | Tracking failed, but the scans keep running in the background. |
Then the **Installation Complete!** screen displays the organization ID and the **Open dashboard** button.
If the Service Principal could not be added to some workspaces (for example, due to Power BI request limits), a notice explains how to complete this later in **Settings › Additional Permissions › Add Service Principal to Workspaces**.
{% endstep %}
{% endstepper %}
***
## How to use
### How to resolve the "Admin Consent Pending" status
1. In the **Required Permissions** step, click **Grant Again (with Admin Consent)** on the pending card.
2. In the Microsoft window, check **Consent on behalf of your organization** and accept. Only tenant administrators see this option.
3. Wait for the automatic check (every 10 seconds) or click **Check Again**. With both cards showing **Granted**, click **Continue**.
### How to skip an optional step
The **Additional Permissions**, **Metrics Source** and **Select Workspaces** steps can be left for later.
1. In the step, click **Skip**.
2. Read the window's notice (for example, **Skip the capacity metrics source?**) and click **Yes, skip step**. To go back, click **Stay on this step**.
3. After the installation, complete what was left pending: [Additional Permissions](/en/power-monitor/configuracoes/permissoes-adicionais.md#how-to-use), [Metrics Source](/en/power-monitor/configuracoes/monitoramento.md#how-to-configure-the-capacity-metrics-source) or workspace selection in *Governance ›* [*Workspaces*](/en/power-monitor/governanca/workspaces.md#workspace-monitoring) (**Workspace Monitoring** button).
### How to resolve the pending Fabric tenant settings
Use this when the installation ended with the notice *"Installation completed with pending items"*.
1. Ask a **Fabric Administrator** to sign in to Power Monitor (first register them in [Users](/en/power-monitor/usuarios.md#create-a-user) as an Administrator).
2. With that account, open *Settings › Additional Permissions* and, on the **Basic Fabric permissions** card, click **Apply settings** and then **Confirm**.
3. Wait up to 15 minutes and click **Check**: the critical settings should appear as **Granted**.
## Next steps
After the installation, follow the [First access](/en/readme/primeiro-acesso.md) guide. In particular:
* **Gateways:** enable gateway monitoring. See [Enable Gateway Monitoring](/en/power-monitor/monitoramento/gateways/ativar-monitoramento-de-gateways.md).
* **Capacities:** if you skipped the Metrics Source, configure it. See [Enable Capacity Monitoring](/en/power-monitor/monitoramento/capacidades/ativar-monitoramento-de-capacidade.md).
* **Capacity governance (pause/resume/change size (SKU)):** see [Configuring Azure permissions](/en/readme/como-instalar-o-power-monitor/configuracao-de-permissoes-no-azure-para-o-power-monitor.md).
## Frequently asked questions
The status is "Admin Consent Pending". What should I do?
Consent was granted only for your user. Click **Grant Again (with Admin Consent)** and, in the Microsoft window, check **"Consent on behalf of your organization"** before accepting. Only tenant administrators can check this option.
Consent fails right at the start with an invalid client error. What could it be?
A common cause is that the Entra ID directory has reached its object quota, which prevents the application from being created. Check with your tenant administrator and, if needed, contact our [support](https://powermonitor.com.br/suporte).
What name does the created application have in Entra ID?
The App Registration is created as **PowerMonitor-APP** and the security group as **PowerMonitor-Group**. They are visible in **Microsoft Entra ID › App registrations** and **Groups**. Do not delete them or remove the application from the group: without them, Power Monitor stops collecting data.
Does the client secret expire?
Yes, like every Entra ID client secret. With the **App secret expiration** permission, Power Monitor warns you before it expires. The credential is replaced in **Settings › Organization**.
## Related pages
* [How to install Power Monitor?](/en/readme/como-instalar-o-power-monitor.md)
* [Manual Installation](/en/readme/como-instalar-o-power-monitor/instalacao-manual.md)
* [Prerequisites](/en/technical-documentation/instalacao/pre-requisitos.md)
* [Settings](/en/power-monitor/configuracoes.md)
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.powermonitor.com.br/en/readme/como-instalar-o-power-monitor/instalacao-automatica.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.